❌

Reading view

There are new articles available, click to refresh the page.

Google dismantles botnet secretly running on 1.3 million Android TV boxes

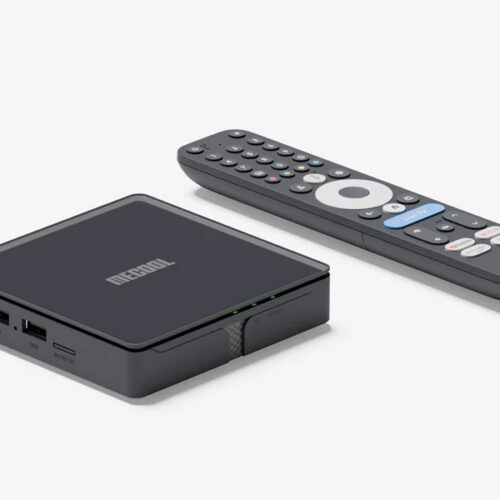
Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says its screening process missed the malware due to "obfuscation techniques" employed by Shenzhen-based Videostrong Technology.

In a detailed blog post, the Threat Intelligence Group explains how the x.cpe botnet evolved quickly from a single-stage dropper into a modular three-stage malware platform that sold access to third parties. Manufacturers must have their devices certified if they want access to Google apps and branding, a process that is supposed to catch threats like this. However, Videostrong's compromised boxes, mostly sold under the MECOOL brand, evaded detection by using a backdoor to remotely install the malware after the devices were set up and online.

After devices appeared online, a stub application called x.cpe or com.oemservice would phone home. This package did not have any malicious capabilities of its own, but it had the system-level permissions necessary to install malware modules at the operator's behest. It also disabled Play Protect, which would have otherwise flagged the silently installed packages as malicious.

Read full article

Comments

© Google

UEFI bootkit infected fully patched Windows machines. Is Microsoft to blame?

In 2023, malware tracked as BlackLotus became the first publicly documented in-the-wild UEFI bootkit capable of bypassing Secure Boot on fully updated Windows 11 systems. With the industry-wide chain-of-trust mechanism subverted, the malware was able to run malicious code before Windows was fully loaded and many security defenses were operational.

Microsoft had already patched the vulnerability that BlackLotus exploited in 2022. In 2023 and 2024, Microsoft issued additional updates. The first added a new certificate that no longer trusted the vulnerable boot managers. The second provided the means to revoke trust in the digital certificate used to sign older vulnerable Windows boot managers. The organizations infected by the new bootkit, which is tracked under the name BlackX, had installed all of these patches. So how did they fall victim?

UEFI bootkit refresher

Before discussing the incident further, a brief review of BlackLotus and UEFI malware is in order. Short for Unified Extensible Firmware Interface, UEFI is firmware that runs immediately after a computer is turned on. One of its main jobs is to load system configuration settings, identify and initialize hardware components, and prepare the computer to start its OS.

Read full article

Comments

© Getty Images

One of Google’s Android partners turned 1.3 million set-top boxes into a botnet

A current Videostrong Android TV device.

Google says one of its Android manufacturing partners secretly built a backdoor in 1.3 million devices and turned them into a botnet. The company says it has now dismantled the backdoor and "cut ties" with the manufacturer, the Shenzhen, China-based Videostrong Technology Co., which has been banned from building or selling certified Android devices or supplying software for them.

The infected devices were used without owners' knowledge for "malicious activity," like ad fraud, data exfiltration, and routing unauthorized network traffic. Google claims the "backdoor and botnet were intentionally developed, deployed, and operated for financial …

Read the full story at The Verge.

Are Freezers Being Hacked? Europe and the U.S. Military Investigate.

A wave of disruptions at grocery stores, which some officials blame on cyberattacks, highlights the vulnerability of supply chains. Shops across Europe were affected again on Monday.

© Fred Tanneau/Agence France-Presse — Getty Images

Shelves were empty at a grocery store in Névez, France, last month after hundreds of supermarket refrigeration systems in the country were targeted.

Are Freezers Being Hacked? Europe and the U.S. Military Investigate.

A wave of disruptions at grocery stores, which some officials blame on cyberattacks, highlights the vulnerability of supply chains. Shops across Europe were affected again on Monday.

© Fred Tanneau/Agence France-Presse — Getty Images

Shelves were empty at a grocery store in Névez, France, last month after hundreds of supermarket refrigeration systems in the country were targeted.

Are Freezers Being Hacked? Europe and the U.S. Military Investigate.

A wave of disruptions at grocery stores, which some officials blame on cyberattacks, highlights the vulnerability of supply chains. Shops across Europe were affected again on Monday.

© Fred Tanneau/Agence France-Presse — Getty Images

Shelves were empty at a grocery store in Névez, France, last month after hundreds of supermarket refrigeration systems in the country were targeted.

More European supermarkets are getting their freezers hacked

Employees empty goods out freezers to load into shopping carts at ICA Kvantum supermarket in Sjoebo, Sweden, on November 2, 2026, after a hacker attack raised the temperature in the freezers to 50 degrees Celsius.
Employees at an ICA Kvantum supermarket in Sjoebo, Sweden, unload spoiled food from the freezer units. | Image: Johan Nilsson / TT News Agency / AFP via Getty Images

Grocery stores across Europe have been hit by another wave of suspected cyberattacks, reporting sudden changes in the temperatures of their fridges and freezers. Major supermarket chains across Belgium, Sweden, Luxembourg, and Estonia were affected, according to local reports shared by Bloomberg and Reuters.

One Ica Kvantum store in Sweden said on its Facebook page that its fridges and freezers had been hacked overnight, with temperatures remotely raised to 50 degrees Celsius (122 Fahrenheit). In a statement to Business Insider, a spokesperson at Swedish supermarket chain Coop also confirmed that "unauthorized actors were able to access and …

Read the full story at The Verge.

Binance Reports $3.64 Billion in Outflows as It Resumes Normal Transactions

The cryptocurrency exchange saw an immediate uptick in customer withdrawals, following the theft of $6.3 billion in tokens that has been linked to North Korea.

© Tyrone Siu/Reuters

Changpeng Zhao, the founder of Binance, at a cryptocurrency conference last year. The company said on Sunday that just 2.1 percent of the assets it manages had been withdrawn.

Anthropic VS code extension on Cursor backdoored for nearly 12 hours

An official extension for Anthropic’s Claude model was backdoored and threatened as many as 5,000 developers' machines, multiple sources reported Friday. Anthropic so far has yet to warn customers of the incident.

The compromised package was a VS Code extension available in the marketplace of Cursor, a maker of AI-assisted developer tools, the company said Friday. The malicious version, 2.1.313, subsequently affected “at most 5,000 users,” presumably when they either downloaded it or their systems automatically fetched and installed it. Anthropic pushed version 2.1.314 several hours after the previous version became available on Cursor, according to independent researcher Kevin Beaumont. Both Beaumont and the CTO and co-founder of security firm Phorion said that version 2.1.313 was distributed through Anthropic’s official account on Cursor. So far, neither Cursor nor Anthropic has explained how the attackers gained control of the account.

In search of cloud credentials

“It was a supply-chain compromise where the attacker gained access to the official distribution channel,” Phorion CTO and co-founder Luke Roberts told Ars. “The malicious version 2.1.313 was posted to the official Anthropic account, effectively superseding 2.1.312. Extensions auto-update in Cursor by default, but users can configure this in settings.” Phorion has more details here.

Read full article

Comments

© Getty Images

Binance’s $6.3 Billion Hack Is Just the Start of a Risky New Era

The largest cyber heist in history came as attackers increasingly use artificial intelligence and other advanced techniques to steal crypto and quickly launder the funds.

© Tyrone Siu/Reuters

The founder of Binance, Changpeng Zhao, in Hong Kong in August. The company, the world’s biggest crypto exchange, has promised to make customers whole.

Binance’s $6.3 Billion Hack Is Just the Start of a Risky New Era

The largest cyber heist in history came as attackers increasingly use artificial intelligence and other advanced techniques to steal crypto and quickly launder the funds.

© Tyrone Siu/Reuters

The founder of Binance, Changpeng Zhao, in Hong Kong in August. The company, the world’s biggest crypto exchange, has promised to make customers whole.

Binance’s $6.3 Billion Hack Is Just the Start of a Risky New Era

The largest cyber heist in history came as attackers increasingly use artificial intelligence and other advanced techniques to steal crypto and quickly launder the funds.

© Tyrone Siu/Reuters

The founder of Binance, Changpeng Zhao, in Hong Kong in August. The company, the world’s biggest crypto exchange, has promised to make customers whole.

Hackers steal $6.3 billion from Binance in record crypto heist

Binance has suspended all withdrawals after the world’s largest cryptocurrency exchange fell victim to what appears to be the biggest heist in history.

The exchange put the “estimated total impact” of the hack at about $6.3 billion and said around $3 billion of affected assets, mainly stablecoins that act as cash for the crypto market, had been frozen.

But analysts at Elliptic said the attacker had changed about $3.3 billion into digital assets that could not be frozen and was working to cash those out as traditional currency.

Read full article

Comments

© Dan Kitwood/Getty

Binance hackers stole $6.3 billion in record-breaking crypto heist

An illustration of falling coins with crypto logos on.
Binance says it will cover all losses resulting from the hack. | Image: Cath Virginia / The Verge, Turbosquid

Binance has disclosed that $6.3 billion worth of crypto funds have been stolen from the platform, in what's believed to be the biggest cryptocurrency hack on record. In a series of updates posted to X, the crypto exchange said that user funds are safe, and that around $3 billion of the impacted assets have been frozen so far.

Binance has publicly committed to covering any losses resulting from the hack. The company has an emergency reserve fund of around $1.3 billion (at last valuation) to protect user assets in these situations, and said it has also reserved over $6.34 billion of company funds to cover this incident - $5 billion of which …

Read the full story at The Verge.

Binance Suspends Withdrawals After Crypto Hackers Steal $6.3 Billion

The crypto exchange said it was compromised in what could be the biggest crypto heist ever. One research lab attributed the theft to “North Korea’s elite hacking unit.”

© Antonio Masiello/Getty Images

Changpeng Zhao, Binance’s founder, said the incident “does look like a hack.”

Binance Suspends Withdrawals After Crypto Hackers Steal $6.3 Billion

The crypto exchange said it was compromised in what could be the biggest crypto heist ever. One research lab attributed the theft to “North Korea’s elite hacking unit.”

© Antonio Masiello/Getty Images

Changpeng Zhao, Binance’s founder, said the incident “does look like a hack.”

Binance Suspends Withdrawals After Crypto Hackers Steal $6.3 Billion

The crypto exchange said it was compromised in what could be the biggest crypto heist ever. One research lab attributed the theft to “North Korea’s elite hacking unit.”

© Antonio Masiello/Getty Images

Changpeng Zhao, Binance’s founder, said the incident “does look like a hack.”

Binance Grapples With ‘Security Incident’ That May Cause $6.3 Billion in Losses

The world’s largest crypto exchange suspended deposits and withdrawals after an apparent hack.

© Antonio Masiello/Getty Images

Changpeng Zhao, Binance’s founder, said the incident “does look like a hack.”

Binance Grapples With ‘Security Incident’ That May Cause $6.3 Billion in Losses

The world’s largest crypto exchange suspended deposits and withdrawals after an apparent hack.

© Antonio Masiello/Getty Images

Changpeng Zhao, Binance’s founder, said the incident “does look like a hack.”

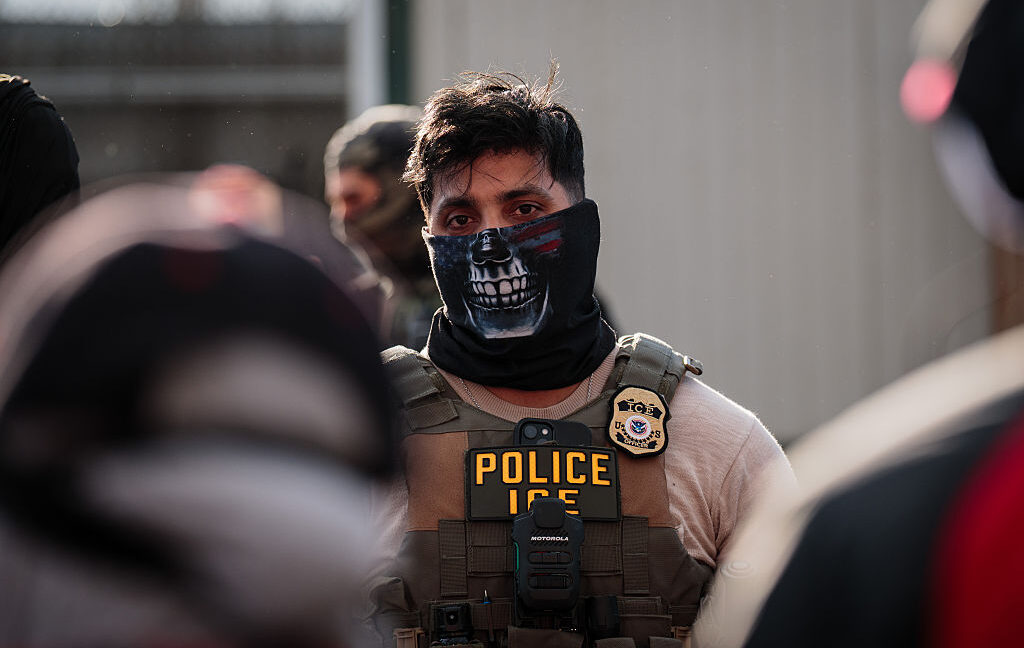
Massive leak exposes 41,000 DHS workers and undercover ICE agents

An unprecedented leak of Department of Homeland Security records has exposed details of more than 41,000 employees or contractors who work for the department and its constituent agencies. The records include email addresses, phone numbers, and office addresses, but also references to internal systems and sensitive information on undercover and surveillance programs. In all, the leak provides a map of how DHS is organized and how it operates.

The records, which span DHS itself as well as seven component agencies, including Immigration and Customs Enforcement and US Customs and Border Protection, were last updated on August 19, 2026. The transparency nonprofit Distributed Denial of Secrets and cybersecurity researcher and journalist maia arson crimew previewed the data for WIRED, which they say they obtained from a group calling itself the Department of Peace.

DDoSecrets published the archive, which it calls “Icepick,” on Wednesday. In a press release, DDoSecrets says the data is from DHS's Okta login system. In a note with the files, the hackers wrote, “They have our information, so it’s only fair that we have theirs.”

Read full article

Comments

© Adam Gray/Getty

❌